
Understanding OAuth Web Server Flow: A Beer Garden Analogy
Welcome back to our Securing Identity Series! In this installment, we delve deeper into the OAuth Web Server Flow, expanding on our previous beer garden analogy while providing detailed insights into the flow’s intricacies.
The Beer Garden Analogy Revisited
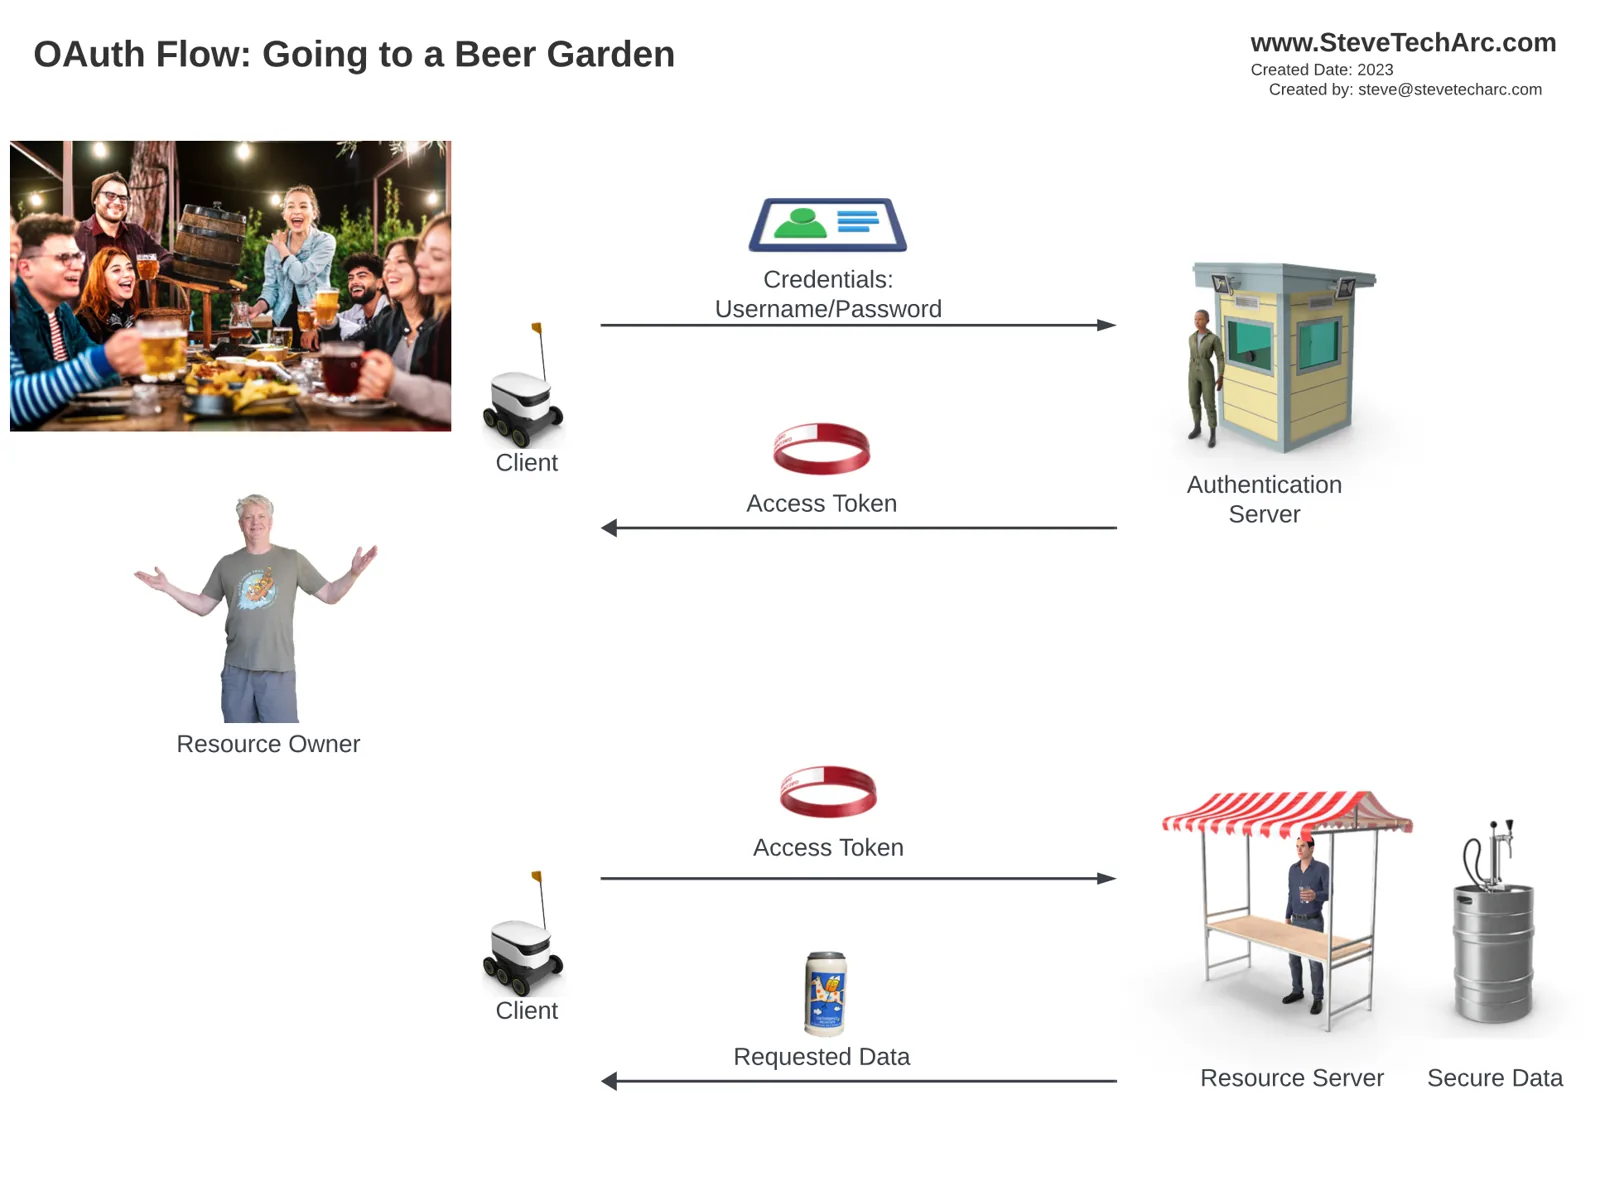
In a previous analogy, we likened the process of obtaining an access token (or a wrist bracelet in our analogy) to ordering beer at a beer garden. The client (a robot) directs you to the authentication server after the resource server denies access due to a lack of an access token. Upon validating your credentials, the authentication server provides an access token, allowing you to access the requested data from the resource server.
Introducing a Third Party: The Burger House
In this extended analogy, we introduce a third party, the Burger House, which needs to access beer from the beer garden using your credentials. This process involves both a front-end channel (less secure, represented in red) and a back-end channel (more secure, represented in black).
Step-by-Step Process:
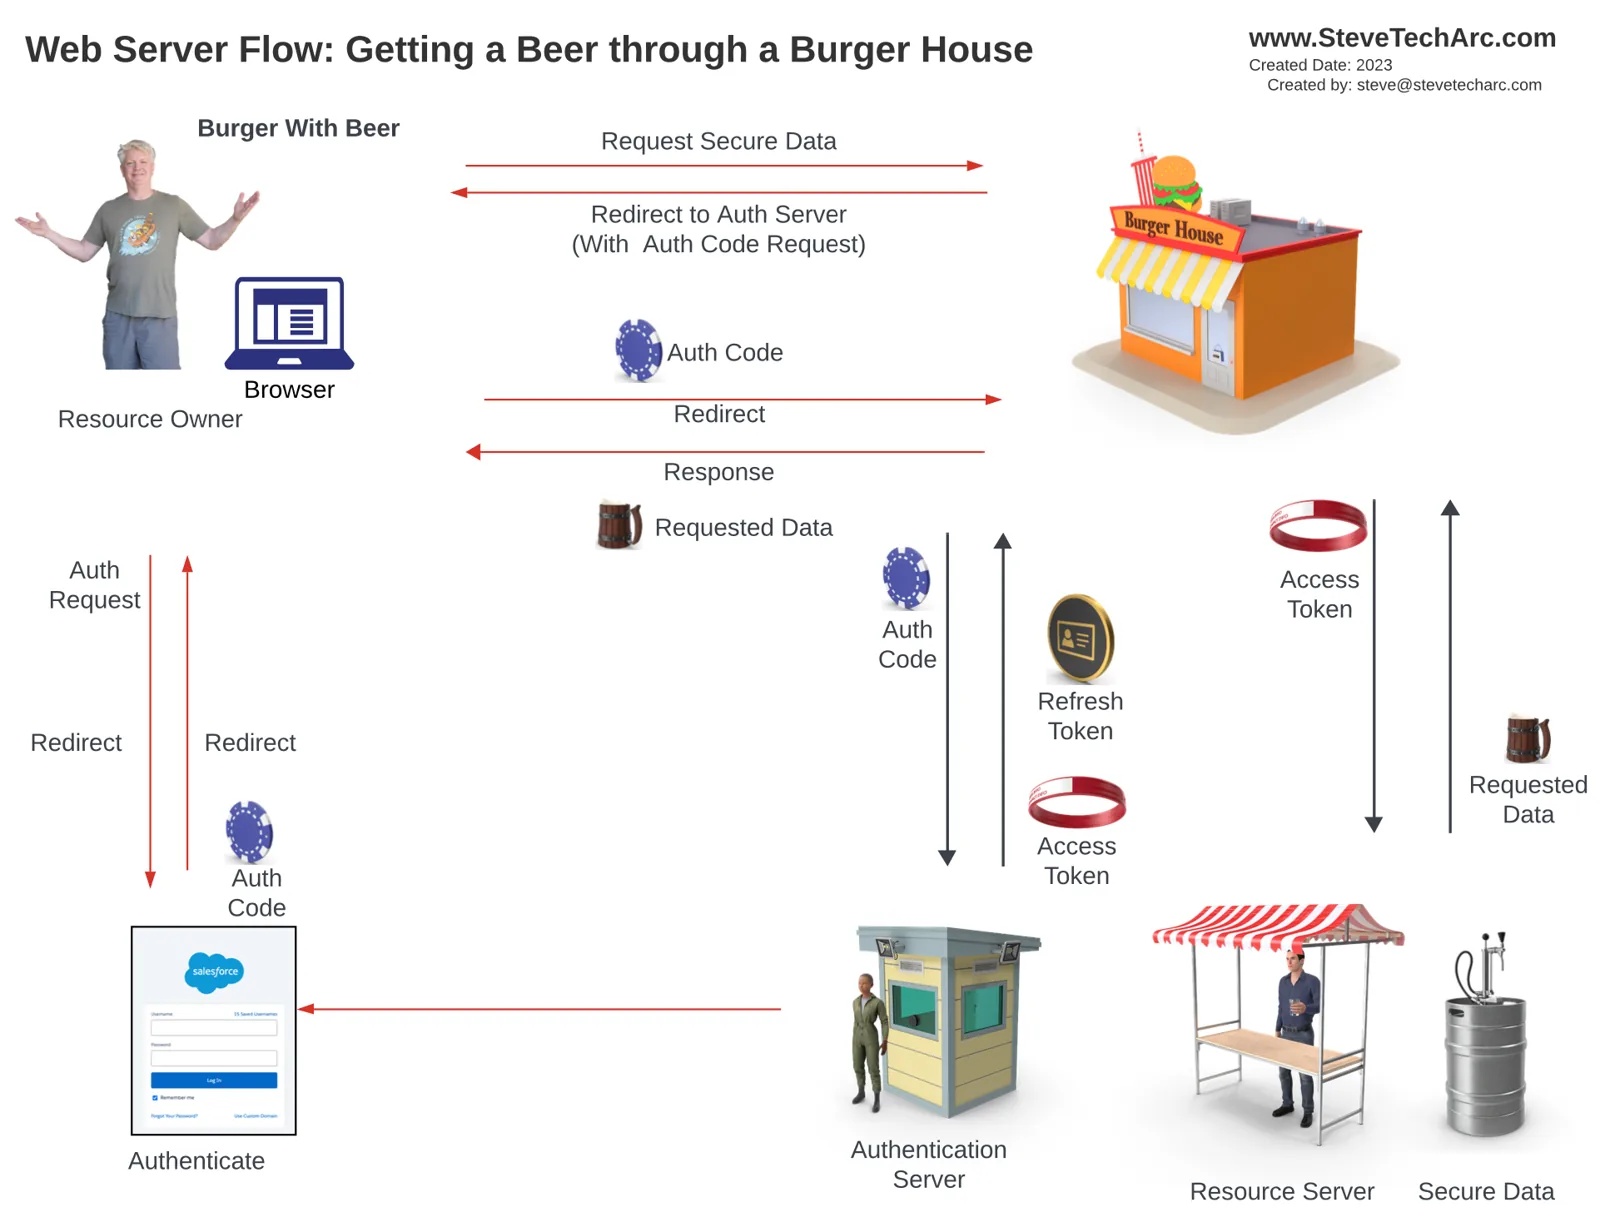
Request at Burger House: You request beer at the Burger House, which doesn’t have it.
Redirection: You are redirected to the authentication server’s public website via a less secure front-end channel.
Authentication: You log into Salesforce, which then issues an authorization code (represented by a blue coin).
Authorization Code Exchange: The Burger House receives the authorization code and presents it to the authentication server via a secure back-end channel.
Token Receipt: The Burger House receives an access token and potentially a refresh token upon successful authentication.
Data Request: Using the access token, the Burger House requests data from the resource server, combines it with its data, and presents it to you.
Key Elements of the OAuth Web Server Flow:
Two Channels: The flow involves a less secure front-end channel and a secure back-end channel.
Authorization Code: A temporary authorization code is used for secure exchanges, then discarded.
Business License: The Burger House must have a special license (consumer key and secret) to operate on behalf of resource owners, ensuring secure and authorized exchanges.
Conclusion
The OAuth Web Server Flow is intricate but crucial for secure data access, especially when third parties are involved. This flow safeguards against potential attacks, ensuring secure transactions and data integrity.
Stay Tuned
Embark on your Salesforce Identity journey with confidence! For more insights and tips, stay tuned here on www.SteveTechArc.com and to the @SteveTechArc (opens in a new tab) YouTube channel. Subscribe and enhance your understanding of Salesforce Identity.
Helping change the world by sharing integration info with fellow Architects and those on their Architect Journey!
STA 3.12